

Penetration testing report templates provide a structured format to document findings and recommendations. Examples of these templates can streamline the reporting process and enhance clarity.
A penetration testing report is essential for organizations seeking to strengthen their cybersecurity. It details vulnerabilities found during testing and offers actionable recommendations. Using a standardized template can improve consistency and ensure all critical areas are covered. Effective reports not only highlight security gaps but also prioritize remediation steps.
They serve as valuable communication tools between technical teams and management. By following established templates, businesses can efficiently convey findings and foster a proactive security culture. Understanding various templates and examples can lead to better security posture and risk management strategies.

Credit: www.yumpu.com
Introduction To Penetration Testing
Penetration testing is a crucial part of security strategies. It identifies weaknesses in systems and networks. Organizations perform these tests to protect sensitive information.
Why Security Testing Is Essential
Security testing is vital for several reasons:
- Identify Vulnerabilities: Find security gaps before attackers do.
- Improve Security Posture: Strengthen defenses against threats.
- Ensure Compliance: Meet legal and regulatory requirements.
- Protect Reputation: Avoid data breaches that harm trust.
Without regular testing, systems remain at risk. This can lead to serious financial losses.
The Role Of Penetration Testing
Penetration testing plays a key role in security. It simulates real-world attacks on systems. This helps to:
- Assess Security Controls: Evaluate how well defenses work.
- Test Incident Response: Check how teams react to breaches.
- Provide Actionable Insights: Deliver clear recommendations for improvement.
Penetration testing gives organizations a roadmap. It shows where to focus efforts for better security.
Credit: www.slideshare.net
Key Components Of A Pentest Report
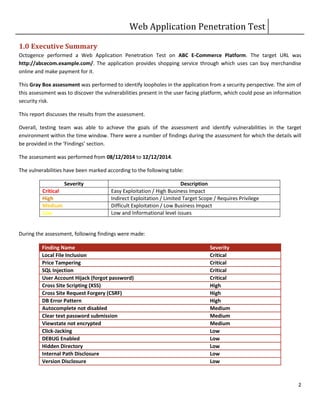
A Penetration Testing (PenTest) report is essential for understanding security weaknesses. It guides businesses in improving their defenses. A well-structured report has key components that make findings clear and actionable.
Executive Summary
The Executive Summary provides a high-level overview of the testing results. It should be concise and easy to understand. Key elements include:
- Objectives: What was the goal of the PenTest?
- Scope: Which systems or applications were tested?
- Key Findings: Major vulnerabilities discovered during testing.
- Recommendations: Suggested actions to improve security.
This section helps stakeholders grasp the important points quickly. Busy executives can make informed decisions based on this summary.
Detailed Findings And Evidence
The Detailed Findings and Evidence section dives deeper into the vulnerabilities. It includes:
- Vulnerability Description: What is the issue?
- Risk Level: Is it low, medium, or high risk?
- Evidence: Screenshots, logs, or code snippets to support findings.
- Impact: What could happen if the issue is not fixed?
- Recommendations: Steps to resolve the issue.
This section provides detailed insights. It allows technical teams to understand and address vulnerabilities effectively.
| Vulnerability | Risk Level | Impact |
|---|---|---|
| SQL Injection | High | Data breach, unauthorized access |
| Cross-Site Scripting (XSS) | Medium | Data theft, session hijacking |
| Weak Password Policy | Low | Increased risk of unauthorized access |
Clear documentation of findings is crucial. It helps teams prioritize fixes and enhance overall security.
Designing An Effective Report Template
Creating a strong penetration testing report template is vital. It helps convey findings clearly. A well-structured report improves understanding. Different audiences need different information. Customization is key for effective communication.
Structure And Clarity
An effective template must have a clear structure. Follow these essential sections:
- Executive Summary: Provide a brief overview of findings.
- Scope: Define what was tested and why.
- Methodology: Explain the testing methods used.
- Findings: List vulnerabilities and issues discovered.
- Recommendations: Suggest fixes for identified problems.
- Appendices: Include detailed data or logs.
Each section should be easy to read. Use bullet points for key information. Keep language simple and direct. Avoid technical jargon unless necessary.
Customizable Sections For Different Audiences
Different stakeholders need different details. Here’s how to customize:
| Audience | Focus Areas |
|---|---|
| Executives | High-level findings, risks, and business impact |
| IT Teams | Technical details, vulnerabilities, and remediation steps |
| Compliance Officers | Regulatory compliance and adherence to standards |
Use visuals like charts for clarity. Visuals can simplify complex information. This approach keeps the audience engaged.
Focus on what each audience needs. Tailor the content for maximum impact. A well-designed report ensures better understanding and action.
Best Practices For Reporting Findings
Effective reporting is key in penetration testing. A clear report helps teams understand security risks. It guides actions to improve systems. Follow these best practices to enhance your reporting.
Prioritizing Vulnerabilities
Not all vulnerabilities are equal. Focus on the most critical issues first. Use a ranking system to categorize them.
Consider factors like:
- Severity: How damaging is the vulnerability?
- Exploitability: Can attackers easily exploit it?
- Impact: What would happen if an attack occurs?
Here’s a simple priority table:
| Priority Level | Description |
|---|---|
| High | Critical vulnerabilities that require immediate attention. |
| Medium | Moderate risks that should be addressed soon. |
| Low | Minor issues that can be fixed later. |
Clear And Actionable Recommendations
Provide specific steps for fixing each vulnerability. Avoid technical jargon. Use simple language to explain solutions.
Your recommendations should include:
- Immediate Actions: Steps to take right away.
- Long-term Solutions: Strategies for permanent fixes.
- Resources: Links to tools or guides.
Example of a clear recommendation:
1. Patch the software to close the security gap.
2. Train staff on recognizing phishing attacks.
Well-structured reports help teams act fast. Clear recommendations lead to better security.
Enhancing Reports With Visuals
Visuals play a crucial role in making penetration testing reports more understandable. They help convey complex data simply and effectively. Using visuals can highlight key findings, making them easier for stakeholders to grasp.