
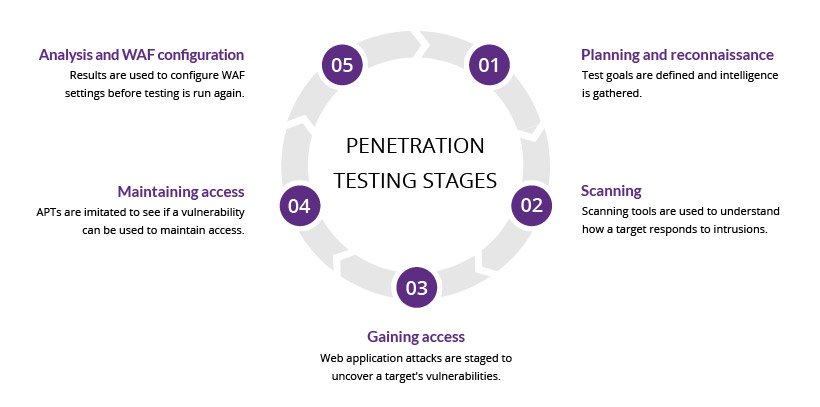
To conduct a web application penetration test, define the scope and gather relevant information about the application. Next, use automated tools and manual techniques to identify vulnerabilities.
How to Conduct a Web Application Penetration Test:Web application penetration testing is essential for identifying security weaknesses in online platforms. As cyber threats evolve, businesses must prioritize protecting sensitive data. A thorough penetration test simulates real-world attacks, highlighting vulnerabilities before malicious actors exploit them. This proactive approach helps organizations comply with regulations and build customer trust.
By regularly conducting these tests, companies can safeguard their digital assets and ensure robust security measures. Understanding how to carry out these assessments effectively can make a significant difference in an organization’s overall cybersecurity posture. Investing in penetration testing is not just a technical necessity; it’s a critical business strategy.
Introduction To Web Application Penetration Testing
Web application penetration testing identifies security weaknesses in applications. This process simulates attacks to find vulnerabilities. It helps businesses protect sensitive data. Understanding this testing is crucial for any organization.
The Importance Of Security Testing
Security testing is vital for several reasons:
- Protects sensitive data: Safeguards user information and business assets.
- Boosts customer trust: Ensures clients feel safe using your services.
- Meets compliance requirements: Adheres to regulations like GDPR and PCI DSS.
- Prevents financial loss: Reduces the risk of costly data breaches.
Investing in security testing saves money in the long run. It helps avoid the expenses related to breaches.
Key Differences From Other Security Assessments
| Feature | Web App Penetration Testing | Other Security Assessments |
|---|---|---|
| Focus | Application vulnerabilities | Network or system vulnerabilities |
| Method | Simulated attacks | Checklist-based evaluations |
| Depth | In-depth analysis | Overview assessments |
| Outcomes | Identifies specific vulnerabilities | General security posture |
Understanding these differences helps prioritize security efforts. Web application penetration testing offers a focused approach. It provides insights that other assessments may overlook.
Preparation For Penetration Testing
Preparation is key to a successful penetration test. Proper planning helps identify vulnerabilities in a web application. It sets the stage for effective testing and reporting.
Setting Clear Goals
Define what you want to achieve with the penetration test. Clear goals help focus the testing effort. Consider these points:
- Identify critical assets.
- Determine potential threats.
- Assess compliance requirements.
- Understand user access levels.
Establishing these goals will guide the entire testing process. Ensure all stakeholders agree on these objectives.
Legal Considerations And Permissions
Legal aspects are crucial in penetration testing. Always obtain written permission from the application owner. This ensures compliance with laws and regulations.
Consider the following:
- Document the scope of the test.
- Define the testing timeframe.
- Clarify liability agreements.
Ignoring legal aspects can lead to severe consequences. Always prioritize legal permissions before starting any test.
Selecting The Right Tools
Choosing the correct tools is vital for effective testing. The right tools help identify vulnerabilities accurately. Here are some popular tools:
| Tool Name | Purpose |
|---|---|
| Burp Suite | Web application security testing |
| Nessus | Vulnerability scanning |
| OWASP ZAP | Automated security testing |
| Metasploit | Exploitation framework |
Evaluate tools based on your goals. Test the tools in a controlled environment first. This ensures they meet your needs.
Understanding The Target Application
Before starting a web application penetration test, it’s vital to understand the target application. This involves analyzing its structure, functionality, and potential vulnerabilities. A thorough understanding helps identify risks and develop effective testing strategies.
Mapping The Application’s Architecture
Mapping the application’s architecture reveals how components interact. This step is crucial for identifying vulnerabilities. Here’s how to do it:
- Identify all components: List all modules and services.
- Understand data flow: Know how data moves through the application.
- Review documentation: Use existing architecture diagrams and documents.
- Use tools: Tools like OWASP ZAP can help visualize the architecture.
Creating a diagram can clarify the application’s structure. Use tools like Lucidchart or draw.io for visual representation. This diagram should include:
| Component | Description |
|---|---|
| Frontend | User interface and client-side interactions. |
| Backend | Server-side logic and database interactions. |
| API | Endpoints for communication between frontend and backend. |
Identifying Entry Points And User Roles
Knowing the entry points helps focus the test. Entry points are where users interact with the application. Here are steps to identify them:
- List user roles: Identify different user types in the application.
- Document entry points: Note where users log in, register, or access features.
- Analyze permissions: Understand what each user role can access.
Entry points may include:
- Login pages
- Forms for data submission
- API endpoints
Each entry point should be tested for vulnerabilities like:
- SQL Injection
- Cross-Site Scripting (XSS)
- Authentication flaws
A clear understanding of user roles and entry points enhances testing effectiveness.
Credit: qualysec.com
Reconnaissance: Gathering Intelligence
Reconnaissance is the first step in a web application penetration test. It involves collecting information about the target. This knowledge helps identify potential vulnerabilities. Two primary methods exist: passive information collection and active information gathering.
Passive Information Collection
Passive information collection involves gathering data without direct interaction. This method keeps you under the radar. Here are some effective techniques:
- Search Engines: Use Google to find information about the target.
- Social Media: Explore social media platforms for user details.
- WHOIS Lookup: Get domain registration information.
- Public Records: Review public databases and reports.
These techniques can reveal useful insights. They may include:
| Data Type | Source |
|---|---|
| Domain Information | WHOIS |
| Email Addresses | Social Media |
| Server Details | Search Engines |
Active Information Gathering
Active information gathering involves direct interaction with the target. This method can be risky but provides deeper insights. Common techniques include:
- Port Scanning: Identify open ports and services.
- Service Enumeration: Discover versions of running services.
- Vulnerability Scanning: Check for known vulnerabilities.
These actions help map the application’s structure. They also expose potential entry points. Always use caution. Unchecked actions may trigger alarms.
Threat Modeling And Risk Assessment
Threat modeling and risk assessment are vital in a web application penetration test. These steps help identify potential security threats and assess risks. Understanding these elements allows teams to prioritize their efforts effectively. This process ensures the web application remai